
The Science of Psychology and Security That Build Foundations for Sustainable Cyber Resilience
Previous Client Success Examples
EXAMPLE #1
Developer Startup with ~50 Employees and outsourced Contractors, fully remote, no cybersecurity program and limited tools, recently added EDR but no customization done for alerts/monitoring, multiple SaaS platforms in use, Google shop, mix of Mac and Linux devices, and must pass SOC II Type 2 Audit within 1 year
Initial 30 to 60 days:
Learning their environment and defining the critical weaknesses that need immediate remediation.
Begin scheduling yearly cyber hygiene activities (Assessments, Evaluations, Testing, Exercises, Trainings, Compliance diligence, etc.).
Defined Audit boundaries and began addressing known issues that would decrease audit success.
3 Months:
Initial Risk and compliance Gap Assessments completed.
Risk report and Risk Register generated. Risk remediation plans established and made trackable.
Gap Assessment report created and disseminated to appropriate teams. Follow up meeting with key employees to delegate gap mitigation tasks using ticketing system.
Investigated, demoed, and onboarded approved MDM technology to reduce Shadow IT overabundance.
Customized logging, monitoring, and alerting within EDR and SIEM. Connected to ticketing system to automate workflows.
Eliminated outdated and excessive elevated user accounts in platform and main network Directories that were not being utilized. Streamlined administration management.
6 Months:
Measurable improvements captured in new KPI Matrix.
Policies and Procedures being updated to match new practices.
Incident Response and Business Continuity Tabletop Exercises performed and reports provided (IR Tabletop scenario customized to a probable attack on their environment from supply chain weaknesses and bypassed threat actor activities). Began establishing more appropriate IR Playbooks based on weaknesses exposed through exercise against critical assets.
Aligned backup practices to Business Impact Analysis results.
Rebuilt operations with automated, accurate, and sustainable practices.
12 Months:
Initiated Audit scheduling with CPA firm. SOC II Type 2 Audit passed with a few minor nonconformities. Utilized report to begin creating year 2 risk remediation roadmap.
Year-end review to show timeline of all completed and still open work. Continued building year 2 roadmap to present to team by 1st week in January.
Recurring meetings occurred every week. More work is conducted than what is shown above, however, a lot of businesses internally struggle to complete this small list, from no fault of the teams. Why not eliminate the stress and bring someone in who is passionate about transforming cybersecurity programs?
EXAMPLE #2
Fintech SMB with ~250 Employees and outsourced Contractors, hybrid environment, outdated cybersecurity program that was never internally shared, some tools in place (Microsoft Purview, Entra ID, Intune, OneDrive) but no logging/monitoring setup, Palo Alto Firewall, website issues with scams/attacks, partial Executive buy-in, a lot of Shadow IT assets on network and excess demo accounts across all teams, Microsoft shop, and must pass SOC II Type 2 Audit within 1 year
All issues above were resolved and audit passed with no findings.
EXAMPLE #3
ECommerce Startup with ~10 Employees, fully remote, 3 inhouse Developers (non-development team and no documented processes/practices), no cybersecurity program, some policies that no one follows, recent EDR implemented on some devices but no logging/monitoring setup, a lot of pushback from all teams on needed changes, a lot of Shadow IT assets being used by everyone, Google shop with some Microsoft productivity tools, ECommerce website and database must be PCI DSS compliant ASAP since customers have been requesting such for a couple years
All issues above were either resolved or planned for year 2 mitigation, due to limited manpower bandwidth. Year 1 PCI audit passed.
Cybersecurity is more than a compliance obligation. Customers expect a certain level of implementation and having it in place can open new doors for accessing new customer industries, especially when you are able to attest that your business operates beneath a strong cybersecurity foundation.
Still not convinced? Take a look at Psyberology’s services or send a question!
Psyberology’s Customized Consulting Services
-
Choice of 3 different packages, depending on hours you need. Designed for Startup, SMB, and Mid-Market businesses.
-
Focusing on compliance controls, evidence gathering, defining audit documentation, and completing annual obligations from your regulation(s), that will help prepare you for the best chance of audit success.
-
For those with various sizes of an IT team, but limited cybersecurity professionals on staff. A custom roadmap is designed based on where you are at today and where you need or want to be within 1 to 3 years.
Any topic can be turned into a roadmap. A few examples of past roadmaps completed — AI security and Governance, Risk Assessments, Incident Response Plan (IRP) Assessment, Account Permissions and Data Security.
-
Just beginning your organization’s cybersecurity journey but do not have the full security budget yet? This will get you started on building a sustainable foundation that will grow with the organization.
What Is Psyberology?
The name PSYBEROLOGY is a crossroad where Psychology and Cybersecurity combine. The name was derived as a portmanteau or blend from the Greek letter ‘Psi’ that is used for social sciences such as Psychology and the professional practice of Cybersecurity. When used together, Psyberology elevates normal cybersecurity practices beyond checkbox security; to build the 5 pillar foundation of where security should begin - People, Technology, Policies, Controls, and Practices.
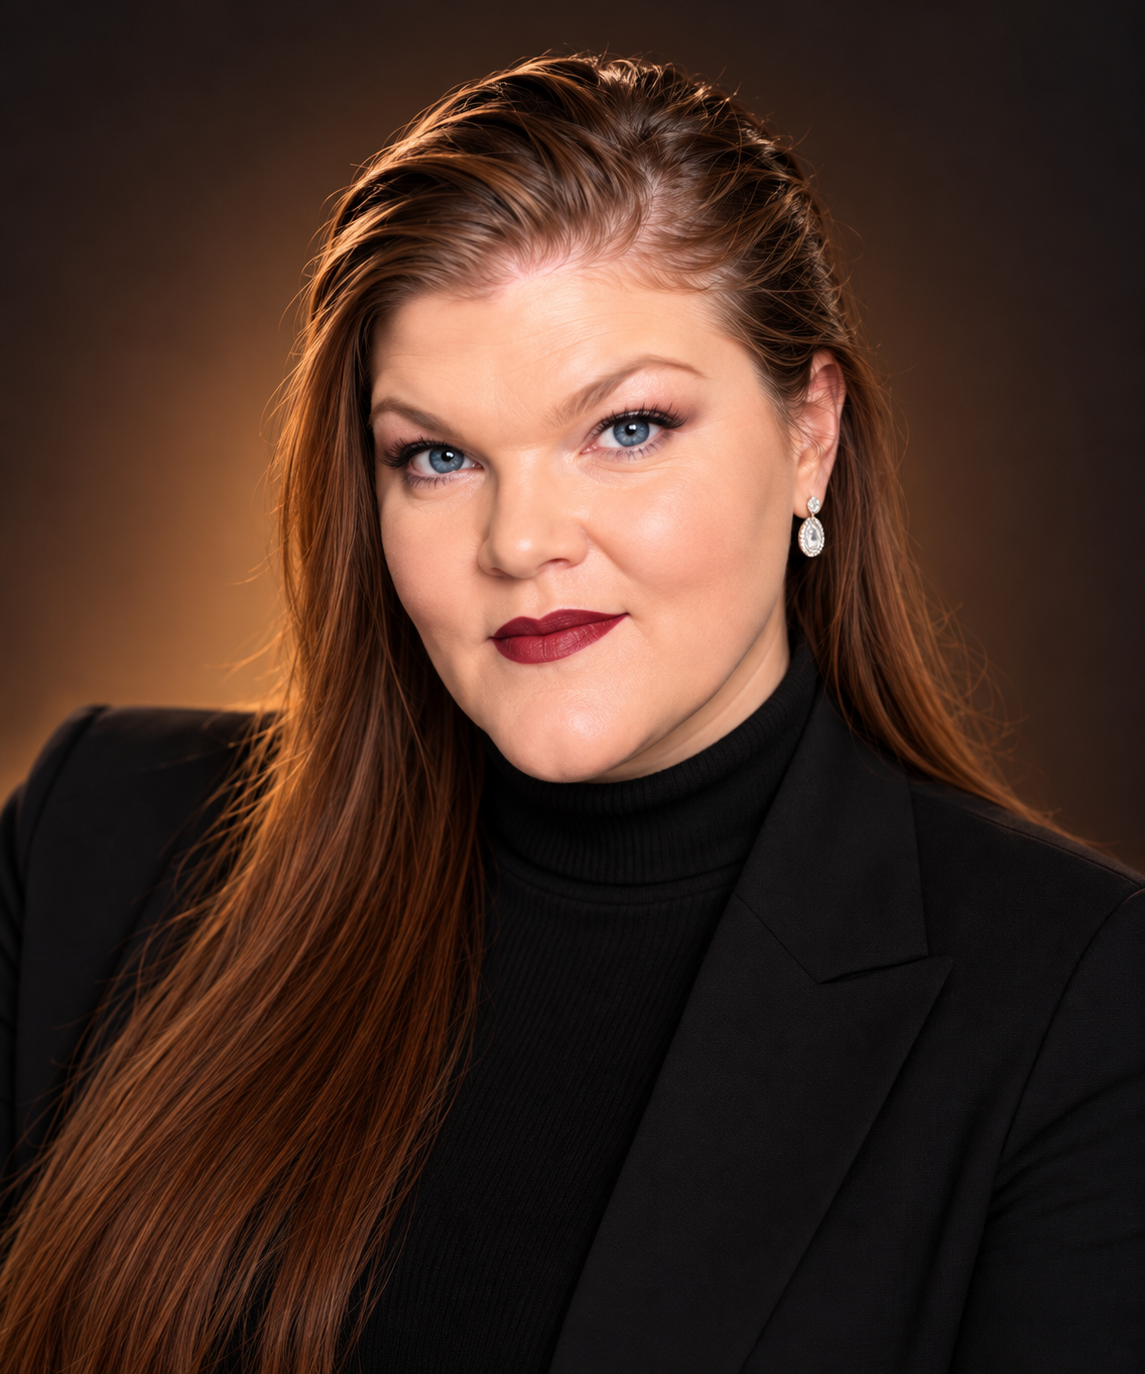
Brandi Wolfe is the Founder and operating consultant at Psyberology; with nearly 20 years experience, most of which spent as a vCISO, and a background working across all industries and business sizes.
Brandi’s cybersecurity background began in the US Marine Corps. Afterwards, time was spent in a few industries such as healthcare and criminal justice, including a degree in Psychology, while maintaining active practice in cybersecurity. Soon after, Brandi decided to make her consulting in cybersecurity official by obtaining a degree in Cybersecurity and Forensics.
Throughout this journey, consistent gaps in how MSPs handle consulting practices began an idea to operate independently. Since the majority of MSPs offer either consulting or hands-on projects, Brandi has specialized in both in order to bring value to clients by converging multiple roles into one vCISO.
She will not only show you what to do, but also how to implement it using a customized, innovative, holistic, and technologically agnostic approach.
Ready to Chat?
Booking your first appointment is easy and safe. The link will provide a pop-up window for the Psyberology Consulting calendar. Choose the day/time you prefer and you are ready to go!
Notifications — You will receive a reminder the day before and another 30 minutes prior to your scheduled meeting.
Follow On LinkedIn
YouTube Video Library
COMING SOON!